
Code quality and security.Coverage gates on every PR.
Codacy is a Coverity alternative built for engineering teams: code quality and security checks on every pull request with nothing to build or host, plus coverage and complexity gates, AI code review and standards that reach the IDE and coding agents.

Trusted by 15,000+ organizations and 200,000+ developers worldwide

Why engineering teams choose Codacy as their Coverity alternative
Quality and security
in the same scan
Codacy checks every pull request for vulnerabilities, vulnerable dependencies, exposed secrets and IaC misconfigurations, and for error-prone code, complexity and duplication in the same scan. Like Coverity, it finds code defects as well as security flaws. Unlike Coverity, it also runs style, complexity and duplication rules on every change, while Coverity is retiring its quality checkers for JavaScript, TypeScript, Python, Go and Kotlin.
Learn more about Code Quality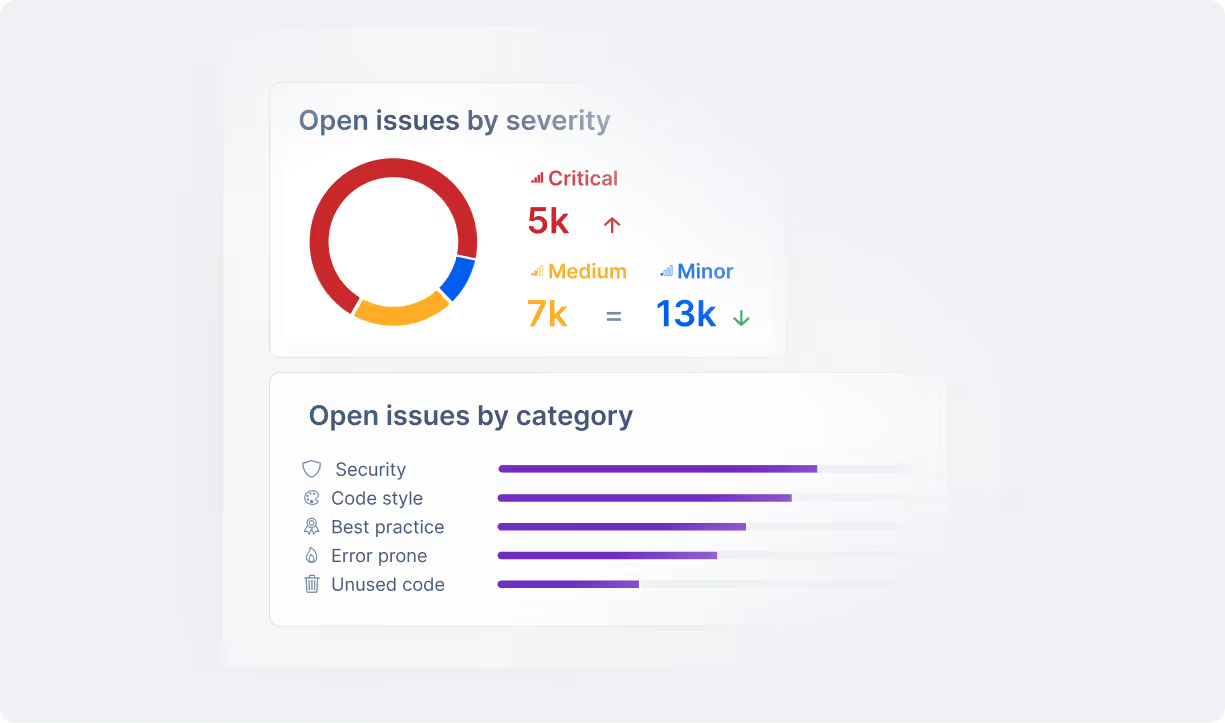
Results on every PR,
nothing to build or host
Codacy scans every commit and pull request on its own infrastructure, triggered by Git webhooks, and posts the results as status checks, with no server to run and no build to capture. Coverity Static Analysis captures your build for compiled languages before each analysis and keeps the results on a Coverity Connect server you host.
Codacy quickstart docs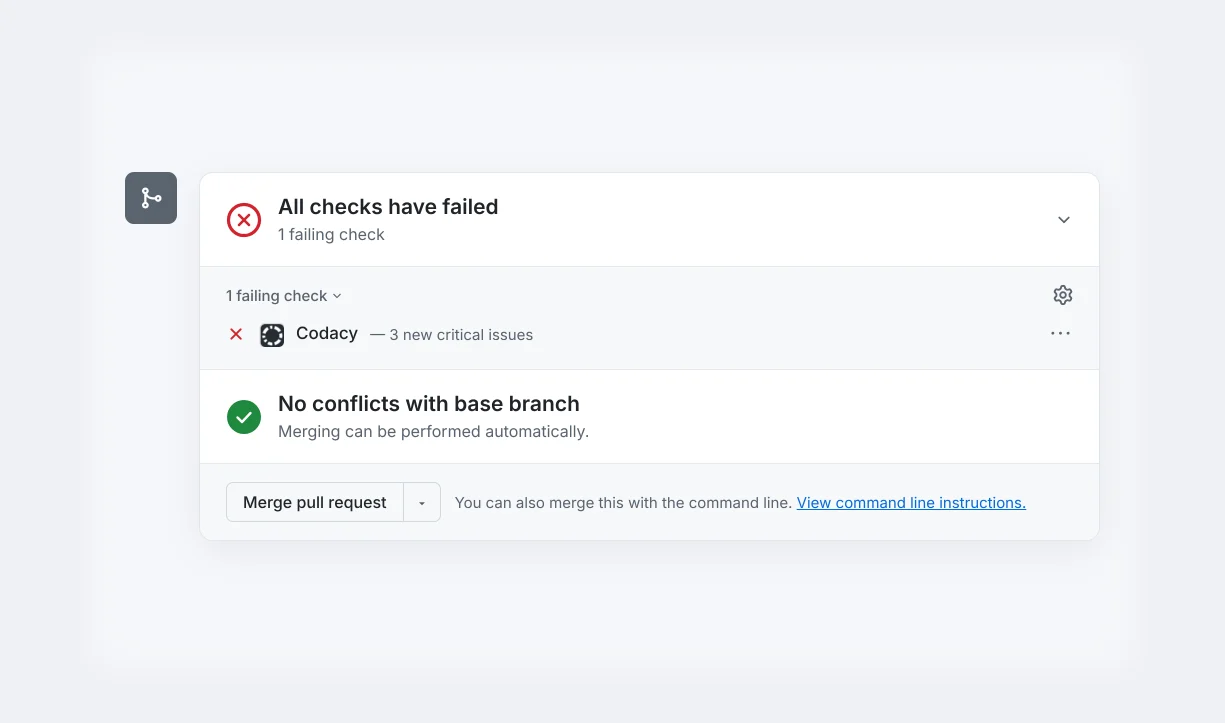
Coverage and complexity gates
on every pull request
Codacy blocks merges that fail your quality or coverage gates, from new critical issues to added complexity, duplication or untested code, and shows how each pull request changes test coverage across every repository. Coverity's gates enforce its defect policy only, and it doesn't track test coverage, so untested changes ship.
See how Codacy coverage works
Standards your agents
run themselves
With Codacy Skills, Claude Code, Codex and Gemini CLI run your Coding Standards locally through the Codacy CLI before commit, and Codacy Guardrails scans AI code as you type. Local analysis needs no account, and your code stays on your machine. Coverity's MCP server for Claude Code and Cursor needs Coverity Static Analysis installed and licensed on each developer's machine.
See Codacy Skills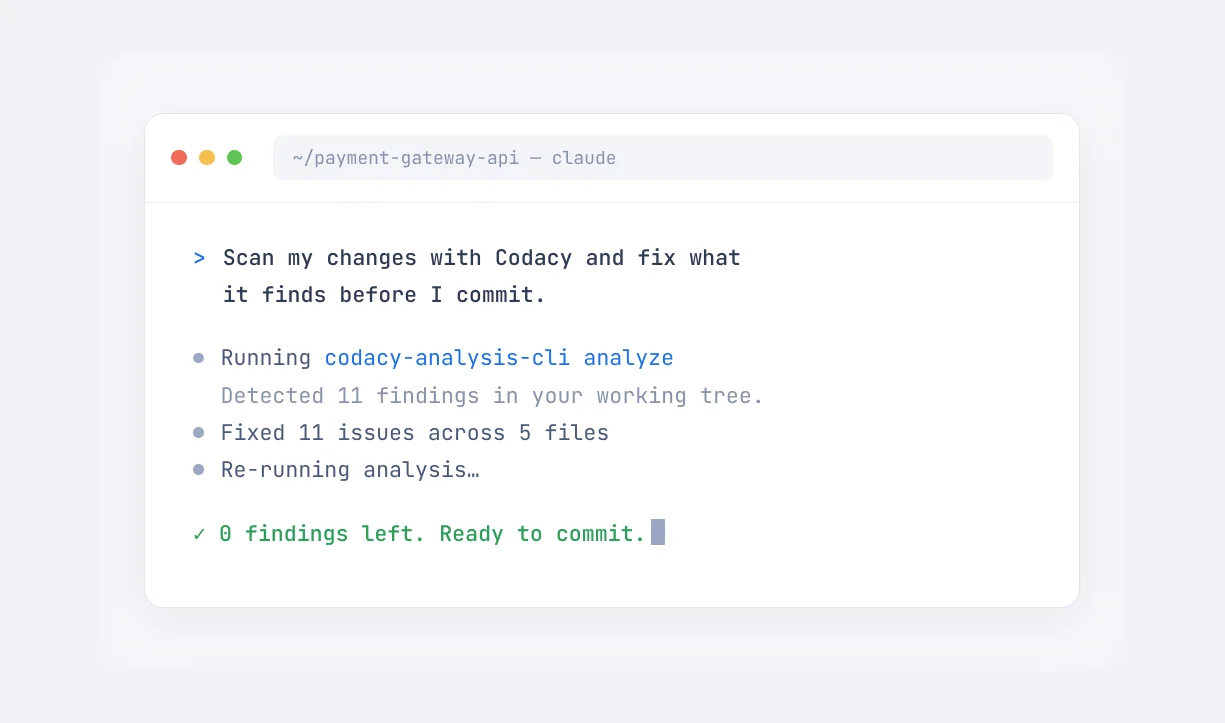
Full scan in minutes
Sign up with your Git provider, add your repositories and get a full scan in minutes, from $18 per developer a month with security, code quality, coverage and AI review included. Coverity is sold by quote, with a 10-user minimum on its AWS Marketplace listing.
See pricing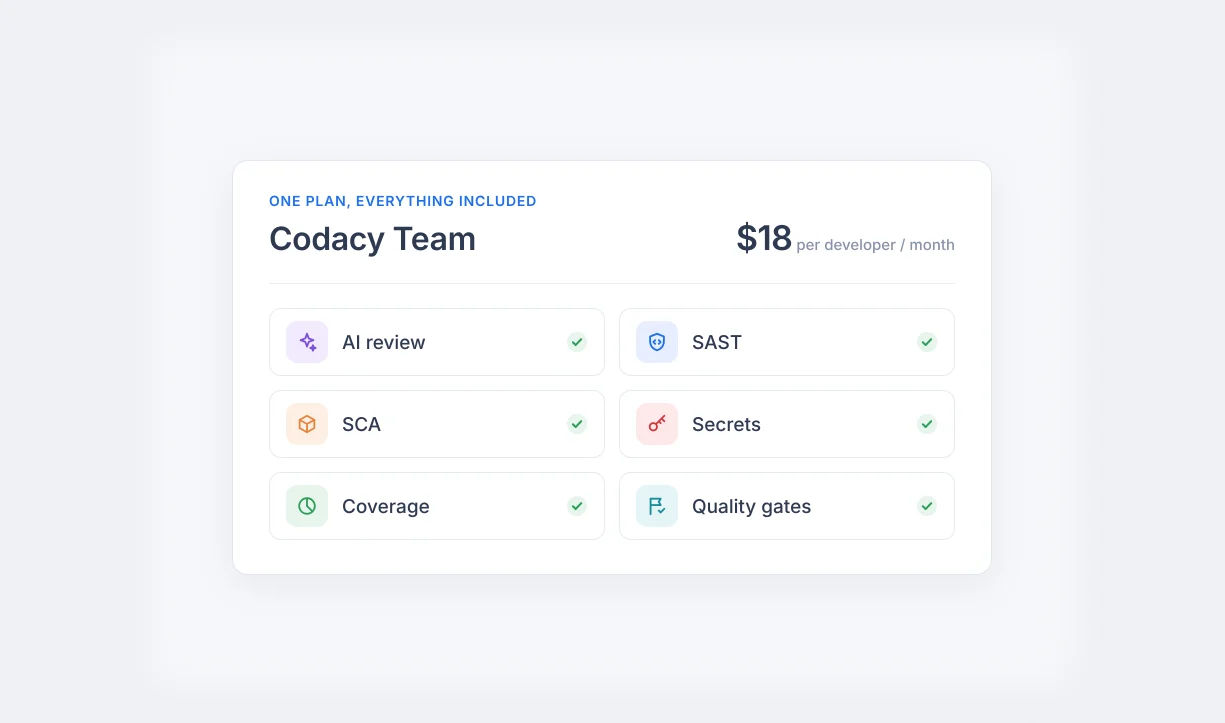
"We blocked the ability to introduce new security issues for the past two years."
Ronen Yurik DevEx Director at LSports
new critical security issues introduced in two years
core repositories standardized under unified quality gates
unit test coverage, from 7% to 70%
Coverity vs Codacy comparison
Code quality and security on every pull request with no build capture or servers, plus coverage and complexity gates in the same platform.

The Coverity column includes features of Black Duck Polaris and Black Duck SCA, which are licensed separately.
When to choose Codacy over Coverity

Teams that want quality and security on every PR
For teams that want vulnerabilities, vulnerable dependencies, secrets and error-prone code caught on every pull request, before they merge. Codacy runs security and quality rules together on every commit and pull request, with one set of Coding Standards for every repository.

Teams tired of build capture and server upkeep
For teams capturing builds and maintaining analysis servers just to keep scans running. Codacy connects to your Git provider and scans every commit and pull request on its own infrastructure, so there is nothing to install, host or upgrade, and code scans never slow your builds.

Teams gating PRs on coverage and complexity
For teams that want untested code, added complexity and duplication caught on every pull request, not just defects. Codacy blocks merges that fail your quality or coverage gates, shows how each pull request changes coverage, and shows which teams are improving.
End-to-End protection,
ready for AI Coding
Today's development teams face complex challenges that traditional tools can't solve.
AI Agent
Enforce secure GenAI code on every prompt


Editor
Scan and auto-fix security and quality issues instantly


Git Repo
Catch risky and untested code before merging


Production
Scan your API endpoints and apps at runtime


Ready to make the switch?
Full scan within minutes | Free trial for 14 days | No credit card required
Built for and loved by devs
Frequently asked questions
How is Codacy's setup and integration different from Coverity?
Connect your GitHub, GitLab or Bitbucket organization in a few clicks, and Codacy scans every commit and pull request on its own infrastructure, posting quality, security and coverage checks to the pull request, with no build to capture and no server to host. The same Coding Standards reach coding agents through Codacy Skills and the IDE through Guardrails. Coverity Static Analysis runs on servers you host or in Black Duck's Polaris cloud, captures your build for compiled languages, and keeps its results in Coverity Connect, so pull request comments, merge blocking and IDE scans each need their own integration.
How does Codacy's billing compare to Coverity?
Codacy's pricing is public and per developer. The Team plan starts at $18 per developer per month billed yearly, and includes code quality, coverage gates, SAST, SCA, secrets and IaC scanning and the AI Reviewer, with unlimited lines of code and scans. Business plans add DAST, license and container scanning, and AI governance. Coverity doesn't publish prices and is sold on a quote. On AWS Marketplace, a Black Duck reseller lists it at $3,375 per team member a year with a 10-user minimum, and SCA, DAST and the Polaris platform are licensed separately.
What assistance does Codacy provide to simplify the migration process from Coverity?
Because Codacy connects straight to your Git provider, you can run it on the same repositories as Coverity and compare results side by side before you switch, with no pipeline to rebuild. Our team maps your Coverity checkers and policies to Codacy coding standards and gate policies and plans the transition with you. The main CI change is sending coverage reports to Codacy, and documentation and personalized onboarding keep your developers shipping while you move.
Can we use Codacy alongside Coverity?
Yes. Codacy adds coverage and complexity gates, maintainability rules and AI code review to every pull request, with one set of standards from coding agents and the IDE to the merge, on Codacy's infrastructure instead of your servers. Teams can keep Coverity for embedded C and C++ code that must meet safety standards such as MISRA, and use Codacy for fast feedback on every pull request across the rest of the codebase. Each tool posts its own checks, and you choose which ones are required.
What kind of technical support is included with a Codacy subscription?
All Codacy subscriptions include responsive, high-quality technical support. Our team of experts is ready to assist you with any questions, from initial setup and onboarding to advanced configuration and troubleshooting. We are committed to ensuring your team is successful with Codacy, providing the reliable assistance you need to keep your development workflow running smoothly.
Is there a no-commitment way to see how Codacy performs on our codebase?
Absolutely. We offer two easy ways to get started. For individual developers and smaller teams, you can start a free 14-day trial. Just connect your repository in minutes and you'll get an instant analysis to see exactly how Codacy performs on your own codebase—no credit card required. For larger organizations and teams evaluating a broader rollout, we offer a dedicated one-month Proof of Value (POV). This extended, guided trial allows you to fully test Codacy's capabilities across multiple teams and repositories with personalized support from our experts. This ensures you can confidently see the value Codacy provides before making any commitment.
What are other Coverity alternatives?
Codacy combines code quality, AppSec and AI guardrails in one platform. Here's how Codacy compares to other tools teams evaluate alongside Coverity:
- Codacy vs GitHub Advanced Security: quality and security from prompt to runtime vs GitHub's security add-ons.
- Codacy vs Wiz: developer-first code security and quality vs a cloud security platform.
- Codacy vs Qodana: quality and AppSec in one platform vs JetBrains' code quality platform.
- Codacy vs Aikido: two all-in-one AppSec platforms compared on quality, coverage and guardrails.
- Codacy vs CodeAnt: AI guardrails and AI risk governance vs AI-first code review.
- Codacy vs DeepSource: two code health platforms compared on coverage, security and pricing.
- Codacy vs Qodo: AI review backed by static analysis and quality gates vs an AI code review platform.
- Codacy vs Greptile: AI review with quality, coverage and security gates vs credit-based AI review.
- Codacy vs Cursor Bugbot: AI review, Guardrails in Cursor and merge gates vs a per-review AI bug finder.
- Codacy vs Veracode: pipelineless security and quality checks on every PR vs upload-based AppSec testing.
- Codacy vs Checkmarx: security, code quality and coverage on every PR vs an enterprise AppSec platform.
- Codacy vs Semgrep: security, quality and coverage gates in one plan vs a developer-first AppSec platform.
- Codacy vs SonarQube: pipelineless cloud scanning and unlimited lines of code vs self-hosted servers.
- Codacy vs Snyk: unified AppSec and code quality vs module-based security pricing.
- Codacy vs CodeRabbit: codebase-wide quality and security vs AI review on open PRs.
Quality and security on every PR,
no build capture or servers.
See it on your code in minutes.
Full scan within minutes | Free trial for 14 days | No credit card required