
SAST, SCA and secrets, on PR and pre-commit.Plus, AI code review you can trust.
Codacy is a Checkmarx alternative built for engineering teams: the SAST, SCA, secrets and IaC scanning you expect, on every pull request and before commit, plus code quality, test coverage and AI code review.

Trusted by 15,000+ organizations and 200,000+ developers worldwide

Why engineering teams choose Codacy as their Checkmarx alternative
SAST, SCA, secrets,
IaC and more
Codacy scans every pull request for vulnerable code, malicious packages, exposed secrets and IaC misconfigurations, and brings the same checks to the IDE, the CLI and coding agents. Like Checkmarx, it scans every push and pull request with no CI step.
See Codacy security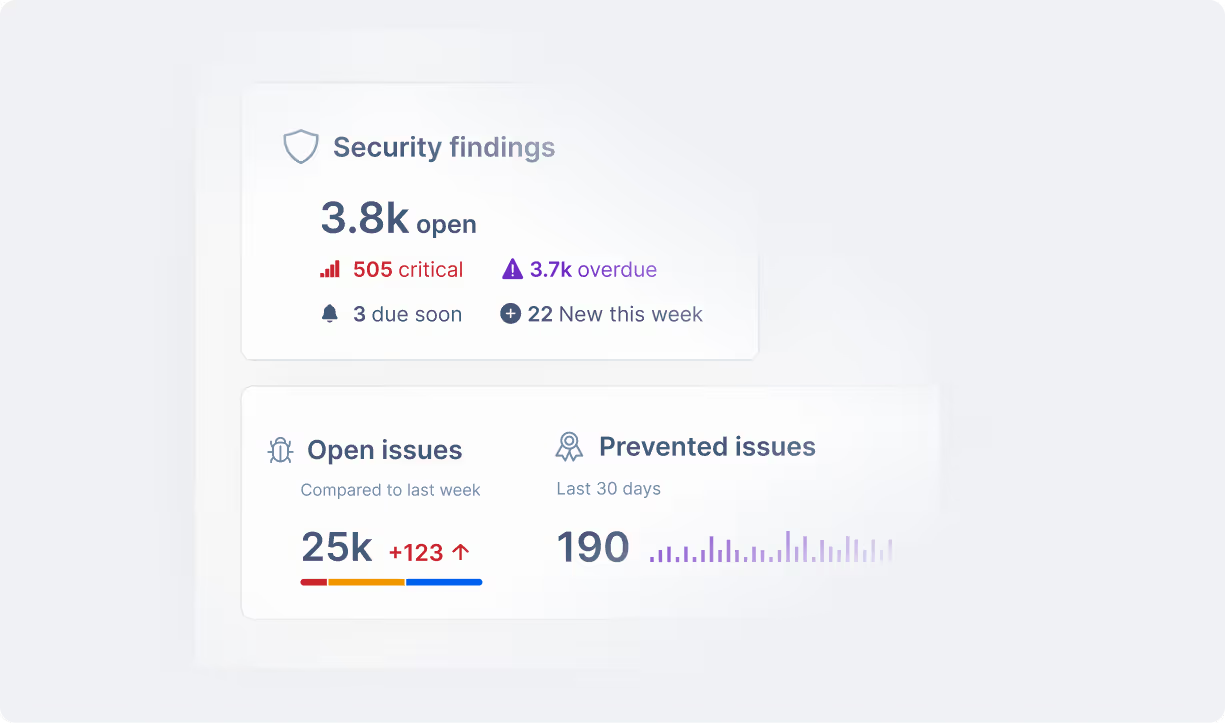
Static analysis you trust,
plus AI that checks intent
Codacy's hybrid AI Reviewer starts with deterministic analysis, so findings on code security, quality and test coverage are consistent and repeatable. Then its AI engine checks the code against what the PR set out to do, flags business logic that was promised but not built, and suggests a precise fix. Checkmarx's AI on pull requests triages and fixes security findings only.
See Codacy AI Reviewer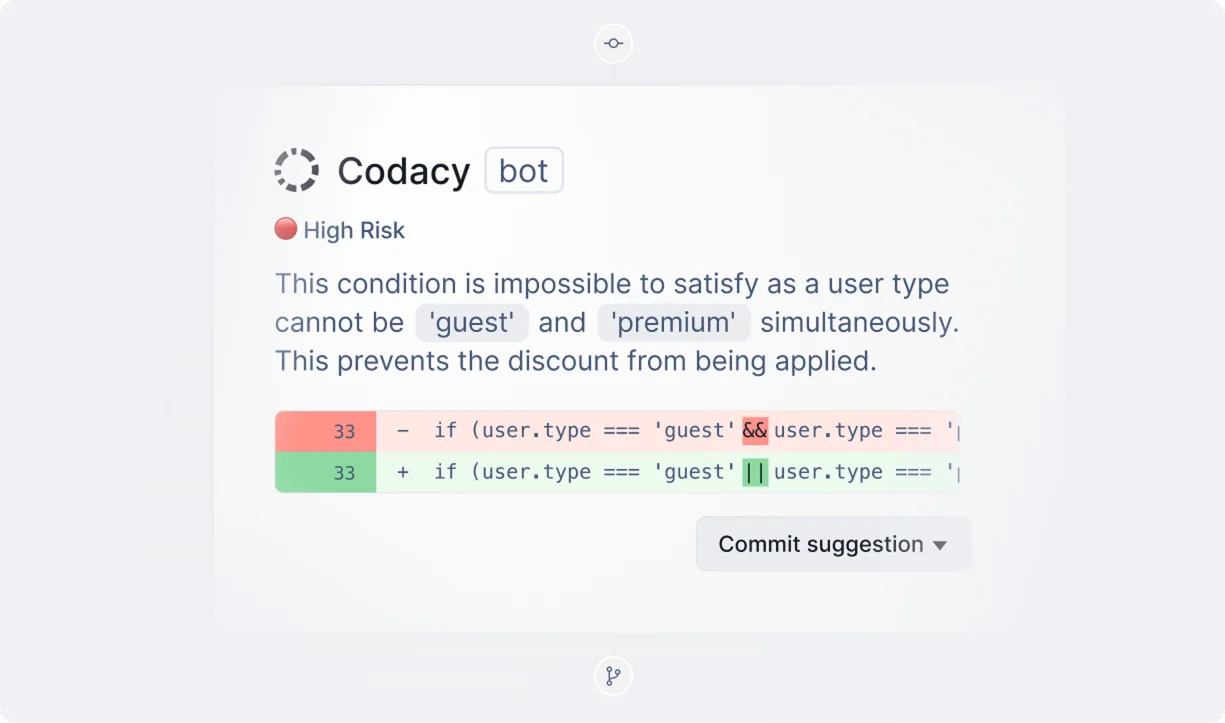
Code health
in the same scan
Codacy checks every pull request for complexity, performance issues and error-prone code in the same scan as your security checks. Checkmarx finds security risks and leaves code quality to other tools.
Learn more about Code Quality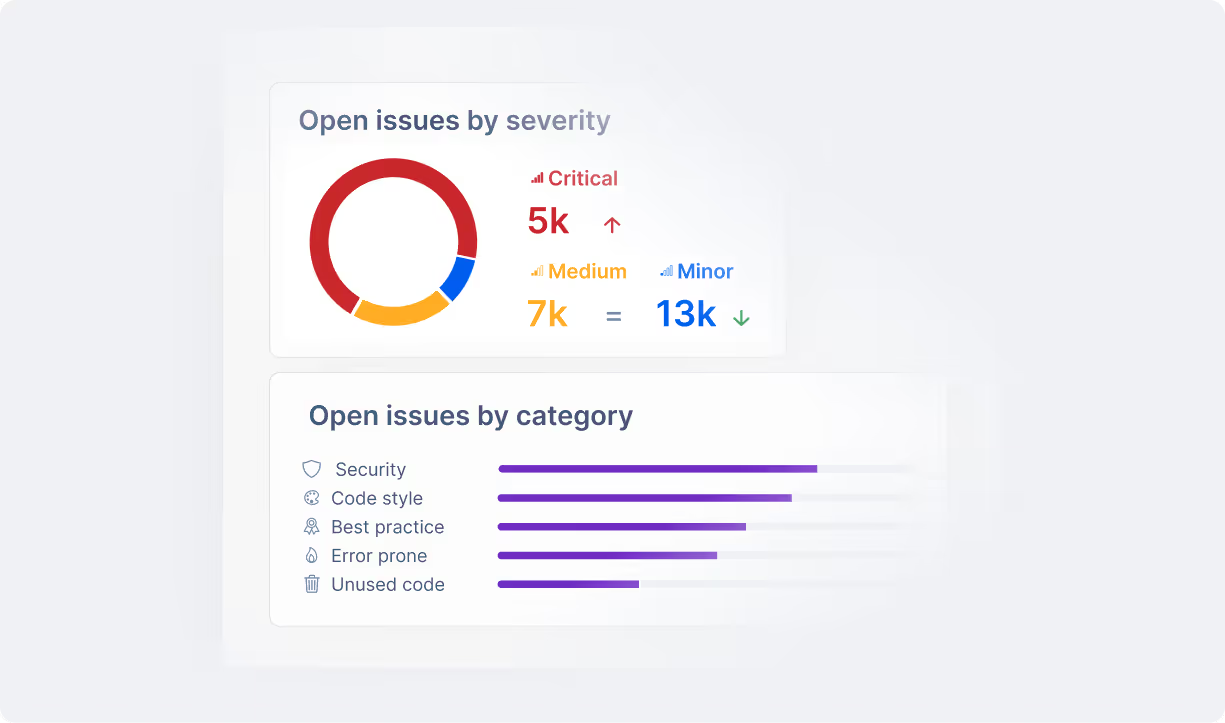
Coverage gates
on every pull request
Codacy shows how each pull request changes test coverage, blocks untested critical code with merge gates, and tracks coverage trends across every repository. Checkmarx doesn't track unit test coverage, so untested changes ship and regressions surface in production.
See how Codacy coverage works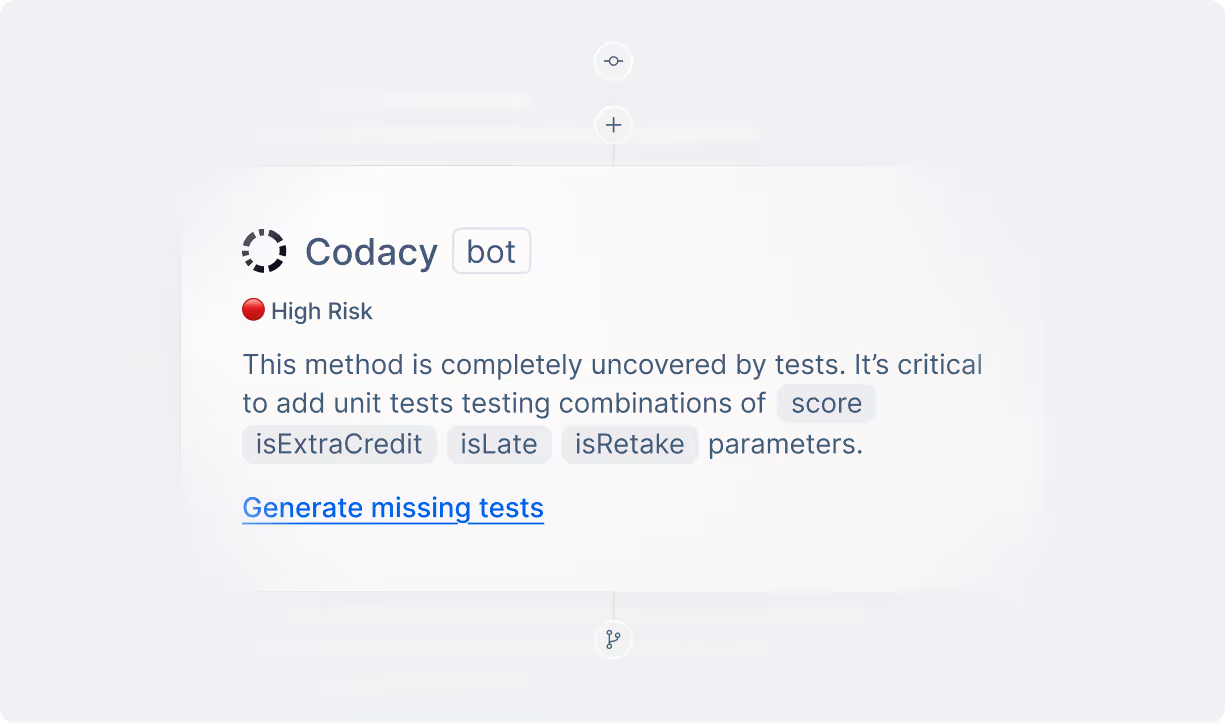
Live in minutes,
no sales call
Sign up with your Git provider and get a full scan in minutes, from $18 per developer a month with security, code quality, coverage and AI review included. Checkmarx is sold through its sales team, with a $30,000 minimum on AWS Marketplace.
See pricing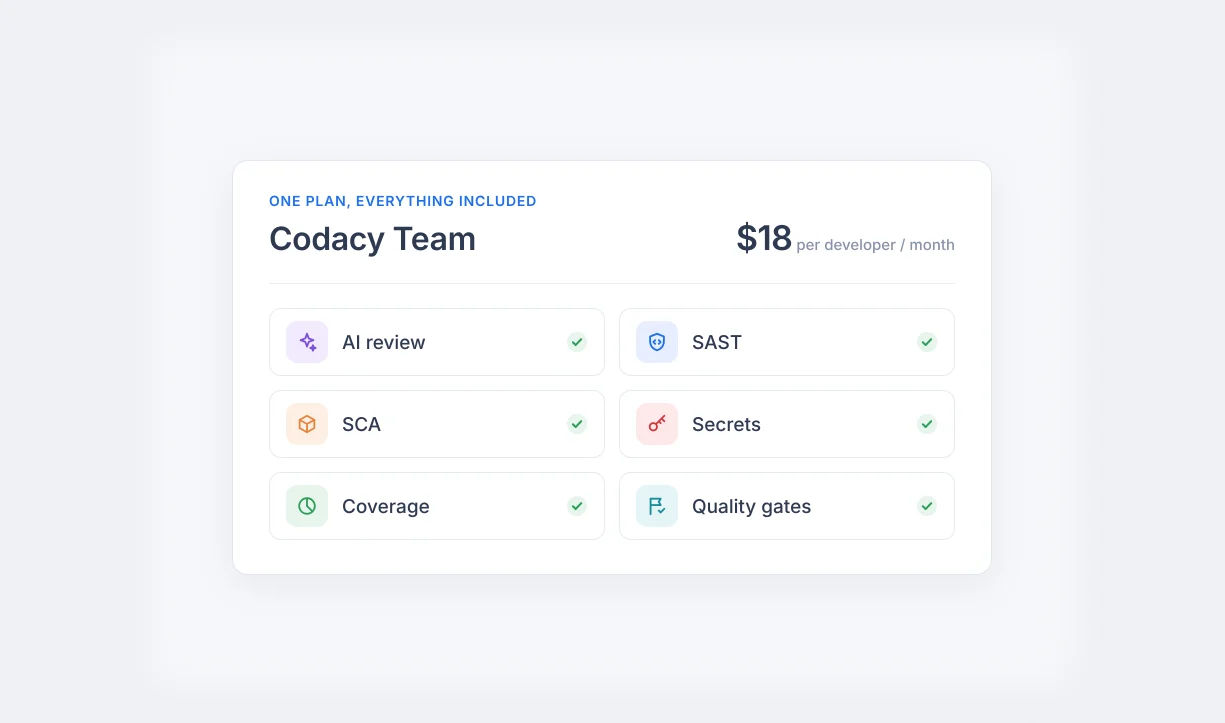
"We blocked the ability to introduce new security issues for the past two years."
Ronen Yurik DevEx Director at LSports
new critical security issues introduced in two years
core repositories standardized under unified quality gates
unit test coverage, from 7% to 70%
Checkmarx vs Codacy comparison
SAST, SCA, secrets and IaC on every pull request and before commit, plus AI code review, code quality and test coverage.

When to choose Codacy over Checkmarx

Teams that want security on every PR
For teams that want vulnerabilities, vulnerable dependencies and secrets caught on every pull request, before they merge. Codacy runs SAST, SCA, secrets and IaC scans on every commit and pull request, and brings the same checks to the IDE and coding agents.

Teams that want AI review on every PR
For teams that want AI on every pull request, with findings that hold up. Codacy's hybrid AI Reviewer starts from deterministic quality, security and coverage checks, then reviews the change itself, its intent, logic and side effects, and suggests a precise fix.

Teams that own maintainability and performance
For teams that want to know when a change makes code harder to maintain, slower or untested. Codacy flags complexity, performance issues and error-prone patterns, tracks test coverage on every pull request, and blocks merges that would ship critical code without tests.
End-to-End protection,
ready for AI Coding
Today's development teams face complex challenges that traditional tools can't solve.
AI Agent
Enforce secure GenAI code on every prompt


Editor
Scan and auto-fix security and quality issues instantly


Git Repo
Catch risky and untested code before merging


Production
Scan your API endpoints and apps at runtime


Ready to make the switch?
Full scan within minutes | Free trial for 14 days | No credit card required
Built for and loved by devs
Frequently asked questions
How is Codacy's setup and integration different from Checkmarx?
Codacy applies one set of Coding Standards, with quality and security rules together, in coding agents through Codacy Skills, in the IDE through Guardrails and on every pull request. You can sign up with your Git provider and get a full scan in minutes, with no sales call. Checkmarx's IDE, agent and pull request scans apply its security policies, so code quality and test coverage need another tool. Like Checkmarx, Codacy scans every push and pull request through your Git provider, with no CI/CD step.
How does Codacy's billing compare to Checkmarx?
Codacy's pricing is public and per developer. The Team plan starts at $18 per developer per month billed yearly, and includes code quality, coverage, SAST, SCA, secrets and IaC scanning and the AI Reviewer, with unlimited lines of code and scans. Checkmarx doesn't publish prices on its website. On AWS Marketplace, Checkmarx One lists at $1,035 to $2,967 per license a year, with a $30,000 minimum, and its licenses count AI agents and bots that commit code.
What assistance does Codacy provide to simplify the migration process from Checkmarx?
Codacy can run on the same repositories as Checkmarx, so you can compare results side by side before you switch. Our team works with you to map your Checkmarx policies to Codacy coding standards and gate policies, and to plan the transition. The main CI change is sending coverage reports to Codacy. We provide documentation and personalized onboarding, so your developers keep shipping while you move.
Can we use Codacy alongside Checkmarx?
Yes. Codacy adds code quality, coverage gates and AI code review to every pull request, with one set of standards from coding agents and the IDE to the merge. Teams can keep Checkmarx for their wider AppSec program, such as API security, and use Codacy for code quality, coverage and developer-facing pull request checks. Each tool posts its own checks, and you choose which ones are required.
What kind of technical support is included with a Codacy subscription?
All Codacy subscriptions include responsive, high-quality technical support. Our team of experts is ready to assist you with any questions, from initial setup and onboarding to advanced configuration and troubleshooting. We are committed to ensuring your team is successful with Codacy, providing the reliable assistance you need to keep your development workflow running smoothly.
Is there a no-commitment way to see how Codacy performs on our codebase?
Absolutely. We offer two easy ways to get started. For individual developers and smaller teams, you can start a free 14-day trial. Just connect your repository in minutes and you'll get an instant analysis to see exactly how Codacy performs on your own codebase—no credit card required. For larger organizations and teams evaluating a broader rollout, we offer a dedicated one-month Proof of Value (POV). This extended, guided trial allows you to fully test Codacy's capabilities across multiple teams and repositories with personalized support from our experts. This ensures you can confidently see the value Codacy provides before making any commitment.
What are other Checkmarx alternatives?
Codacy combines code quality, AppSec and AI guardrails in one platform. Here's how Codacy compares to other tools teams evaluate alongside Checkmarx:
- Codacy vs GitHub Advanced Security: quality and security from prompt to runtime vs GitHub's security add-ons.
- Codacy vs Wiz: developer-first code security and quality vs a cloud security platform.
- Codacy vs Qodana: quality and AppSec in one platform vs JetBrains' code quality platform.
- Codacy vs Aikido: two all-in-one AppSec platforms compared on quality, coverage and guardrails.
- Codacy vs CodeAnt: AI guardrails and AI risk governance vs AI-first code review.
- Codacy vs DeepSource: two code health platforms compared on coverage, security and pricing.
- Codacy vs Qodo: AI review backed by static analysis and quality gates vs an AI code review platform.
- Codacy vs Greptile: AI review with quality, coverage and security gates vs credit-based AI review.
- Codacy vs Cursor Bugbot: AI review, Guardrails in Cursor and merge gates vs a per-review AI bug finder.
- Codacy vs Veracode: pipelineless security and quality checks on every PR vs upload-based AppSec testing.
- Codacy vs SonarQube: pipelineless cloud scanning and unlimited lines of code vs self-hosted servers.
- Codacy vs Snyk: unified AppSec and code quality vs module-based security pricing.
- Codacy vs CodeRabbit: codebase-wide quality and security vs AI review on open PRs.
SAST, SCA and secrets on PR and pre-commit, plus AI code review you can trust.
See it on your code in minutes.
Full scan within minutes | Free trial for 14 days | No credit card required