
Quality as strict as security.AI code held to your standards.
Codacy is a Wiz Code alternative built for engineering teams: the SAST, SCA, secrets and IaC scanning you expect, plus code quality, test coverage and AI code review.

Trusted by 15,000+ organizations and 200,000+ developers worldwide

Why engineering teams choose Codacy as their Wiz Code alternative
SAST, SCA, secrets,
IaC and more
Codacy scans every pull request for vulnerable code, malicious packages, exposed secrets and IaC misconfigurations, and posts the results as status checks with no CI step. Like Wiz Code, it connects to your Git provider in a few clicks and brings security checks to the IDE, the CLI and coding agents through MCP.
See Codacy security
Code health
in the same scan
Codacy checks every pull request for complexity, performance issues and error-prone code in the same scan as your security checks. Wiz Code finds security risks and leaves code quality to other tools.
Learn more about Code Quality
Coverage gates
on every pull request
Codacy shows how each pull request changes test coverage, blocks untested critical code with merge gates, and tracks coverage trends across every repository. Wiz Code doesn’t track unit test coverage, so untested changes ship and regressions surface in production.
See how Codacy coverage works
Static analysis you trust,
plus AI that checks intent
Codacy’s hybrid AI Reviewer starts with deterministic analysis, so findings on code security, quality and test coverage are consistent and repeatable. Then its AI engine checks the code against what the PR set out to do, flags business logic that was promised but not built, and suggests a precise fix.
See Codacy AI Reviewer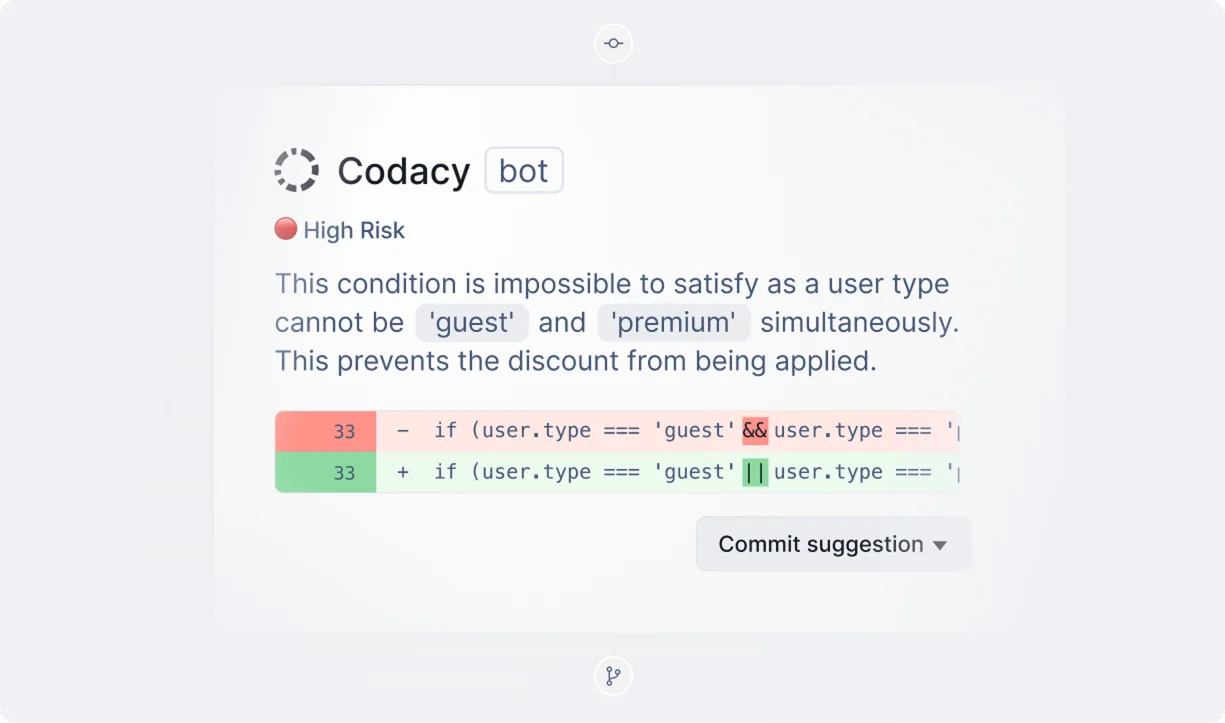
Your full standards,
run locally
With Codacy Skills, coding agents run your full Coding Standards, including code quality and security, through the Codacy CLI before commit, so AI-written code meets your whole bar before it ever reaches a pull request. Wiz Code’s plugins, skills and CLI check for security issues only.
See Codacy Skills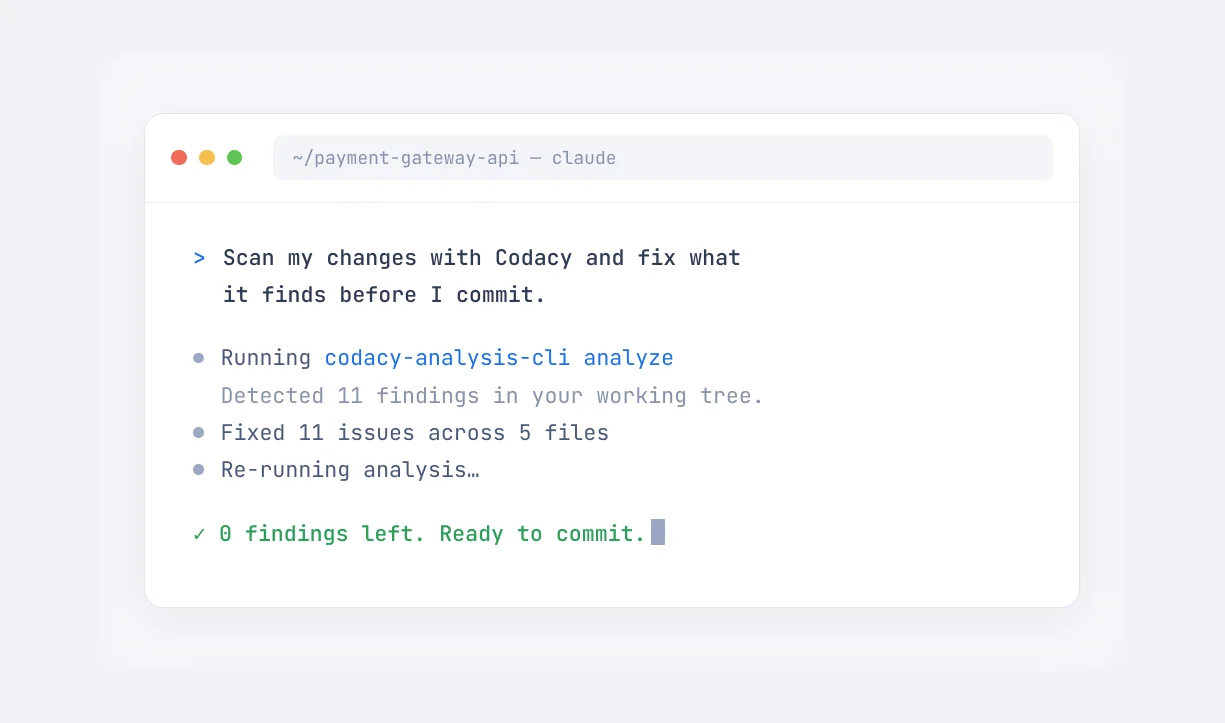
"I can't think of a situation where you wouldn't want to use Codacy unless you were sacrificing quality for speed."
Bryan Cannon Senior Software Engineer at O.C. Tanner
faster code analysis and fixes
cost savings on development
engineers across two countries using the platform

Wiz Code vs Codacy comparison
Everything you expect from Wiz Code's code scanning, plus code quality, test coverage and AI code review.

When to choose Codacy over Wiz Code

Teams that want security findings in full context
Codacy runs the same checks you rely on in Wiz Code: SAST, SCA, secrets, IaC and malicious package detection, on every pull request and in the IDE. Then the hybrid AI Reviewer takes those findings and reviews the change itself, its intent, logic and side effects. Developers get one review that explains what to fix and why.

Teams that own maintainability and performance
Wiz Code finds security risk, but it won't tell you when a change makes code harder to maintain, slower or untested. Codacy flags complexity, performance issues and error-prone patterns across 49 languages and tracks test coverage on every pull request. It blocks merges that would ship critical code without tests.

Teams shipping AI-generated code
Wiz Code's agent plugins check AI-written code for security issues. With Guardrails and Codacy Skills, coding agents follow your full coding standards (security and quality) before they commit. AI Coding Policies then flag issues like unapproved model calls on every pull request.
End-to-End protection,
ready for AI Coding
Today's development teams face complex challenges that traditional tools can't solve.
AI Agent
Enforce secure GenAI code on every prompt


Editor
Scan and auto-fix security and quality issues instantly


Git Repo
Catch risky and untested code before merging


Production
Scan your API endpoints and apps at runtime


Ready to make the switch?
Full scan within minutes | Free trial for 14 days | No credit card required
Frequently asked questions
How is Codacy's setup and integration different from Wiz Code?
Both connect to your Git provider in a few clicks and scan pull requests with no CI/CD step, and both scan in the IDE, from a CLI and inside coding agents. The difference is what runs there. Codacy applies one set of Coding Standards, with quality and security rules together, in coding agents through Codacy Skills, in the IDE through Guardrails and on every pull request. Wiz Code's CLI, plugins and pull request scans apply Wiz security policies only. Codacy also needs no cloud platform: sign up with your Git provider and get a full scan in minutes.
How does Codacy's billing compare to Wiz Code?
Codacy's pricing is public and per developer. The Team plan starts at $18 per developer per month billed yearly, and includes code quality, coverage, SAST, SCA, secrets and IaC scanning and the AI Reviewer, with unlimited lines of code and scans. The free Developer plan runs security and quality scans in your IDE, while Wiz's IDE extension needs a Wiz Code license. Wiz doesn't publish prices on its website. Its AWS Marketplace listing sells Wiz Code as an add-on to Wiz Cloud, at $58,500 a year per 100 licenses.
What assistance does Codacy provide to simplify the migration process from Wiz Code?
Moving your code checks to Codacy takes no pipeline changes or agents. Connect your GitHub, GitLab or Bitbucket organization, choose your repositories, and Codacy runs a full scan within minutes. Our team works with you on a transition plan, sets up coding standards and quality gates that match your current security policies, and helps you send coverage reports from CI. You can run Codacy alongside Wiz Code while you evaluate.
Can we keep Wiz for cloud security and use Codacy for our code?
Yes. Codacy covers the code your engineers and AI agents write: SAST, SCA, secrets and IaC scanning, code quality, test coverage, AI code review and AI coding policies, in coding agents, in the IDE and on every pull request. Wiz Cloud covers your cloud, from infrastructure to runtime. Teams can keep Wiz for the cloud and move code scanning, quality and coverage to Codacy.
What kind of technical support is included with a Codacy subscription?
All Codacy subscriptions include responsive, high-quality technical support. Our team of experts is ready to assist you with any questions, from initial setup and onboarding to advanced configuration and troubleshooting. We are committed to ensuring your team is successful with Codacy, providing the reliable assistance you need to keep your development workflow running smoothly.
Is there a no-commitment way to see how Codacy performs on our codebase?
Absolutely. We offer two easy ways to get started. For individual developers and smaller teams, you can start a free 14-day trial. Just connect your repository in minutes and you'll get an instant analysis to see exactly how Codacy performs on your own codebase—no credit card required. For larger organizations and teams evaluating a broader rollout, we offer a dedicated one-month Proof of Value (POV). This extended, guided trial allows you to fully test Codacy's capabilities across multiple teams and repositories with personalized support from our experts. This ensures you can confidently see the value Codacy provides before making any commitment.
What are other Wiz Code alternatives?
Codacy combines code quality, AppSec and AI guardrails in one platform. Here's how Codacy compares to other tools teams evaluate alongside Wiz Code:
- Codacy vs GitHub Advanced Security: quality and security from prompt to runtime vs GitHub's security add-ons.
- Codacy vs Snyk: unified AppSec and code quality vs module-based security pricing.
- Codacy vs Aikido: two all-in-one AppSec platforms compared on quality, coverage and guardrails.
- Codacy vs SonarQube: pipelineless cloud scanning and unlimited lines of code vs self-hosted servers.
- Codacy vs CodeAnt: AI guardrails and AI risk governance vs AI-first code review.
- Codacy vs DeepSource: two code health platforms compared on coverage, security and pricing.
- Codacy vs Qodana: quality and AppSec in one platform vs JetBrains' code quality platform.
- Codacy vs CodeRabbit: codebase-wide quality and security vs AI review on open PRs.
Code security,
plus quality and coverage.
See it on your code in minutes.
Full scan within minutes | Free trial for 14 days | No credit card required